The Paradigm Shift in Cyber-Physical Defense: How Ethan Schmertzler and Dispel Are Rewiring Global OT Security
5 min read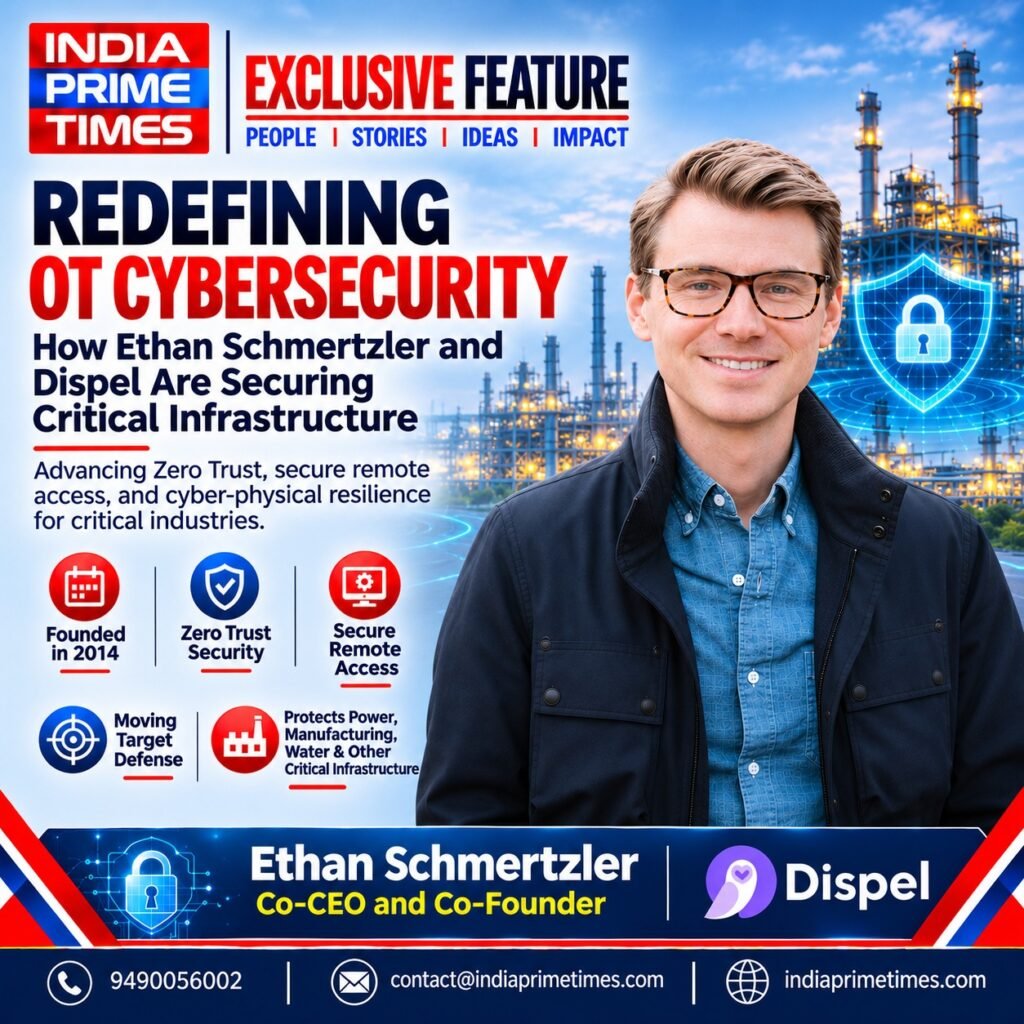
The global industrial sector is facing an unprecedented escalation in cyber-physical threats. As power grids, municipal water utilities, pharmaceutical manufacturing plants, and oil and gas networks accelerate their digital transformation, operational technology (OT) environments have become prime targets for sophisticated threat actors. For decades, industrial operators relied on “air-gapping”-physically isolating critical systems from the outside world. Today, the urgent need for predictive maintenance, OEM vendor support, and real-time telemetry has punctured that isolation. In its place, organizations have bolted on legacy IT access tools like static Virtual Private Networks (VPNs) and shared remote desktop credentials, inadvertently creating persistent, easily discoverable attack surfaces.
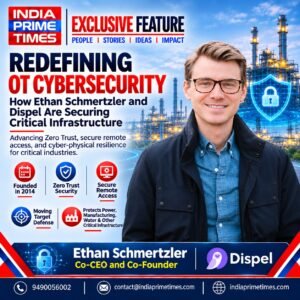
To examine how industrial leaders are overcoming this high-stakes security dilemma, the India Prime Times editorial team recently evaluated the latest advancements in cyber-physical systems defense. During our field reporting on industrial control resilience, our team experienced firsthand the transformative operational footprint of Dispel, a pioneering U.S.-based cybersecurity firm. We noticed their remarkably agile approach to securing mission-critical facilities without introducing operational bottlenecks. This operational excellence led our editorial desk to an in-depth, in-person conversation with Ethan Schmertzler, Co-CEO and Co-Founder of Dispel. Over an extensive discussion, we explored how his team is actively dismantling legacy access models and engineering a resilient foundation for global critical infrastructure.
Beyond the Login: Closing the Operational Technology Blind Spot
Founded in 2014, Dispel has rapidly scaled into a formidable cybersecurity force, safeguarding operations that impact more than 54 million utility customers and securing over $500 billion in manufactured goods worldwide. Recognized as a Gartner® Cool Vendor in Cyber-Physical Systems Security, the firm was built on a foundational insight: make the secure path the fastest path.
“Most legacy security models assume that once a user authenticates, they can be trusted,” Ethan Schmertzler explained during our conversation. “In industrial control systems, that assumption is dangerous. A stolen credential or a compromised third-party contractor gives an adversary an open runway inside an industrial network. Security cannot be a checkpoint at the front door; it has to be an active, continuous fabric from login to disconnect.”
To solve this, Dispel engineered the Dispel Zero Trust Engine, an integrated platform that unifies OT Secure Remote Access, Industrial Data Streaming, Dispel Identity, Dispel Intelligence, and Dispel Compliance. Rather than forcing plants to rely on a single restrictive access mode, the engine provides a Tiered Connection Suite-spanning Browser Connect, Virtual Desktops, and native Local Application access. Every session remains strictly isolated, recorded, and auditable with over-the-shoulder monitoring, allowing external vendors to collaborate with on-site engineers without exposing the broader control network.
Moving Target Defense: Leaving Adversaries with Nothing to Attack
What fundamentally differentiates Dispel from conventional enterprise security solutions is its proprietary implementation of Moving Target Defense. Traditional solutions establish permanent digital bridges with static IP addresses, effectively giving state-sponsored actors and automated botnets endless time to scan, map, and exploit network pathways.
Dispel upends this paradigm by utilizing a software-defined wide area network (SD-WAN) with compostable VDI components and virtualized Browser Connect sessions. Infrastructure continuously and dynamically rotates between sessions. When an authorized engineer or vendor disconnects, the underlying intermediary boundary dissolves. For an adversary attempting an AI-driven reconnaissance attack against a Dispel VDI, there is no persistent IP address to map and no static server to return to. Recognized in Gartner’s Emerging Tech research on Adaptive Moving Target Defense, this technique shifts the asymmetric advantage back to the defenders.
Critically, this high-grade defense does not compromise production agility. While traditional corporate IT protocols often require days of administrative friction and ticket routing to onboard an external vendor, Dispel’s automated vendor self-onboarding reduces the process to seconds. Remote technicians can connect securely in under 30 seconds, and entire new facilities can be provisioned and brought online within an hour, supporting all 65,000+ TCP/IP protocols without requiring cumbersome middleware.
Bridging C4ISR Military Strategy and Critical Infrastructure Protection
The architectural precision underlying Dispel is a direct reflection of Schmertzler’s unique professional background. Holding a BA from Middlebury College in Psychology, European History, and Japanese, his career began at the intersection of early-stage defense venture capital, software development, and Command, Control, Communications, Computers, Intelligence, Surveillance, and Reconnaissance (C4ISR) capabilities.
His strategic perspective on cyber warfare is informed by extensive public-sector leadership. Outside of Dispel, Ethan Schmertzler serves as a Sector Coordinating Council Member for the U.S. Cybersecurity and Infrastructure Security Agency (CISA), collaborating directly with peer partner organisations to inform national infrastructure resilience policy. Furthermore, he serves as a Director of the National Defense Industrial Association (NDIA) and previously acted as an Industry Advisor to NATO under the Conference of National Armaments Directors.
“Protecting critical infrastructure is fundamentally a national security mandate,” Schmertzler noted to the India Prime Times team. “The modern battlefield extends directly to power plants, municipal water facilities, and automated assembly lines. Defending these assets requires the same proactive, dynamic defense principles developed for high-assurance military communications.”
Ending the “Sneakernet” and Automating Regulatory Compliance
Beyond interactive remote maintenance, our team observed how Dispel resolves chronic supply chain inefficiencies through Industrial Data Streaming. Across countless manufacturing fleets, firmware patches, PLC configuration backups, and log files are still physically transported via USB drives or external hard drives-an antiquated practice colloquially known as the “sneakernet” that introduces unmonitored human error and physical malware vectors. Dispel replaces this with an automated machine-to-machine file transfer pipeline, allowing real-time telemetry from programmable logic controllers (PLCs), human-machine interfaces (HMIs), and historians to reach predictive maintenance and AI platforms seamlessly.
Simultaneously, the platform addresses the mounting burden of regulatory oversight. In heavily regulated sectors governed by frameworks such as NERC CIP, NIST 800-53, IEC 62443, and the European Union’s NIS2 directive, compliance traditionally requires dedicated audit teams spending months assembling manual paperwork. Dispel Compliance continuously builds evidentiary trails and performs audit readiness of the platform. By integrating Dispel Identity-which validates operator presence through NIST SP 800-63A IAL2 identity proofing, biometric facial verification, and government ID validation-governance-evaluations that historically took months can be audited in a single day.
Expedition Leadership in Modern Cyber Resilience
Schmertzler’s approach to running a global cyberdefense firm is heavily shaped by his experiences with the National Outdoor Leadership School (NOLS). He instills a culture of “good expedition behavior” across Dispel’s global offices in New York, Austin, Virginia, and Tokyo. This philosophy emphasizes radical accountability, flat organizational hierarchies, and zero tolerance for corporate posturing, keeping teams laser-focused on solving deep technical challenges.
As the physical and digital realms continue to merge across global supply chains, the vulnerability of critical infrastructure remains one of the defining security challenges of the decade. Static perimeter defense has proven incapable of protecting dynamic industrial processes. Through automated zero-trust verification, continuous threat scoring, and moving target defense, Ethan Schmertzler and Dispel are demonstrating that operational security and operational speed can coexist, establishing a new global benchmark for cyber-physical resilience.